Cryptographic keys,
tokens & passwords on demand.
A precision tool for developers and the security-minded: generate high-entropy passwords, hex keys, URL-safe tokens and PINs — then audit any password's strength. Nothing ever leaves the browser.
How long does it take to crack a password?
A short password falls instantly, however random it looks. The table and chart below model an offline attack at 10,000,000,000 guesses per second against a fast hash — the same maths a cracking rig actually runs.
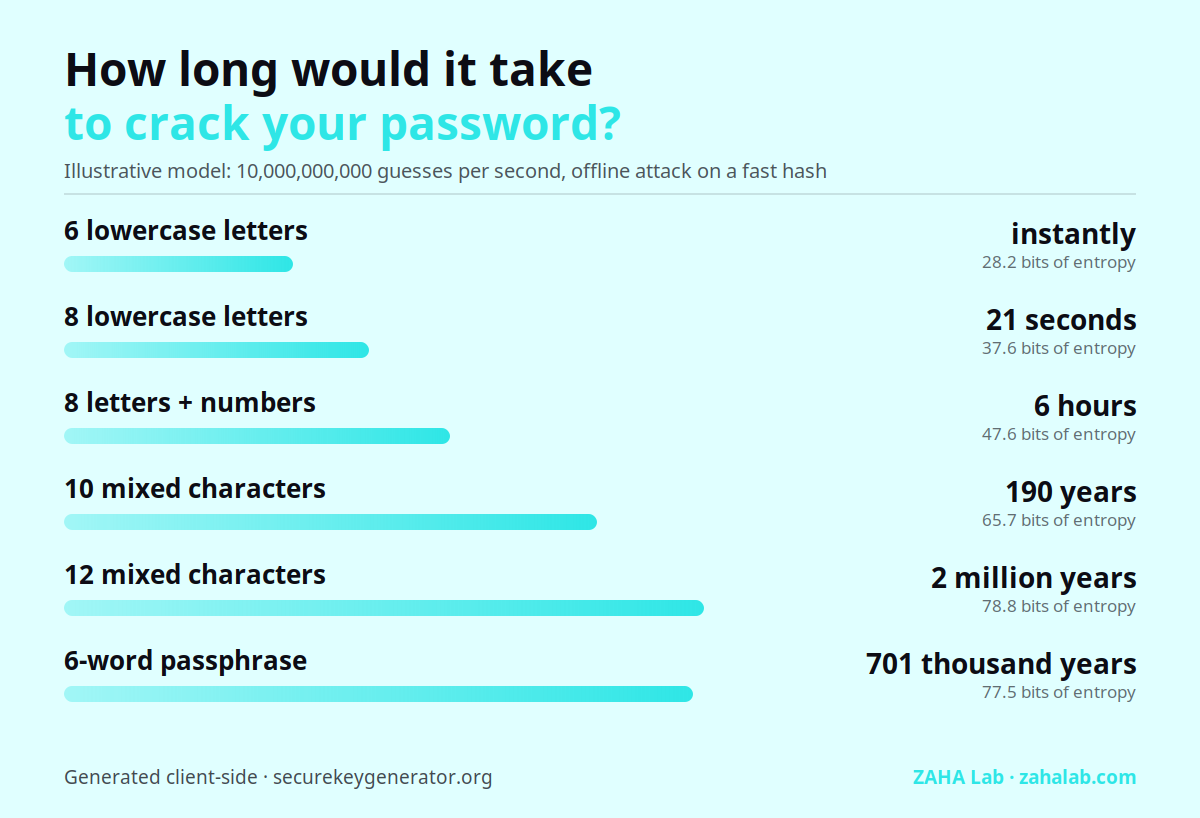
| Password pattern | Time to crack | Entropy (bits) | Verdict |
|---|---|---|---|
| 6 lowercase letters | instantly | 28.2 | Weak |
| 8 lowercase letters | 21 seconds | 37.6 | Weak |
| 8 letters + numbers | 6 hours | 47.6 | Moderate |
| 10 mixed characters | 190 years | 65.7 | Moderate |
| 12 mixed characters | 2 million years | 78.8 | Strong |
| 6-word passphrase | 701 thousand years | 77.5 | Strong |
Assumes uniform random characters and no rate limiting. Password reuse or a breach database shortcut all of the above — which is why a unique password per account matters more than length alone.
Key Generator
// fresh value generated on load
·········
Strength Audit
// analysed locally, never transmitted
Engineered for trust
The guarantees behind every value this tool produces.
CSPRNG only
Every byte is drawn from crypto.getRandomValues(), with rejection sampling to remove modulo bias.
Stateless & local
No backend, no storage, no logging. Open dev-tools — the network tab stays empty.
Four output formats
Passwords, hex secrets, URL-safe tokens and numeric PINs — one tool for every key you need.
The reference desk
Technical writing on entropy, keys and secure randomness.
📊 What Is Password Entropy, Really?
The one number that decides how long a key resists brute force — derived from scratch.
read →⚠️ Common Password Mistakes and How to Avoid Them in 2026
Most password security failures come from the same handful of mistakes.
read →📋 Password Security Best Practices for 2026
A comprehensive guide to password security best practices for 2026.
read →Store what you generate
Keep your generated passwords synced everywhere with NordPass — a zero-knowledge password manager we trust and recommend.